Entitlements
Least privilege, checked on every action and reviewed on a schedule.
Six roles as default privilege bundles, per-account permissions to view, propose, trade and approve, and per-user privileges such as authoring or approving compliance rules. The check runs on the server for every action, refusals say what is missing, and the AI helps keep access tight.
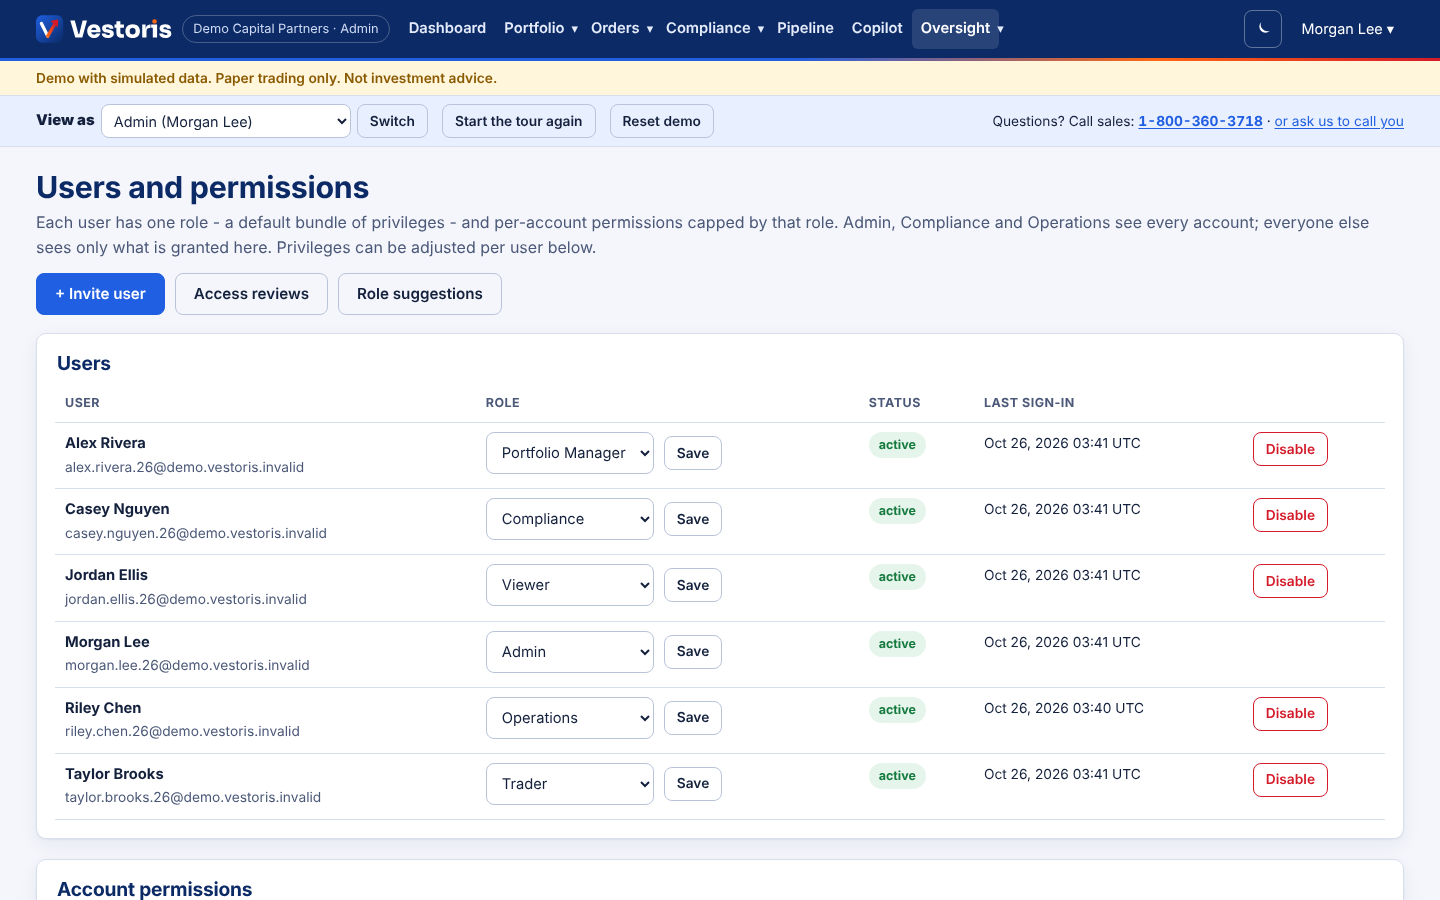
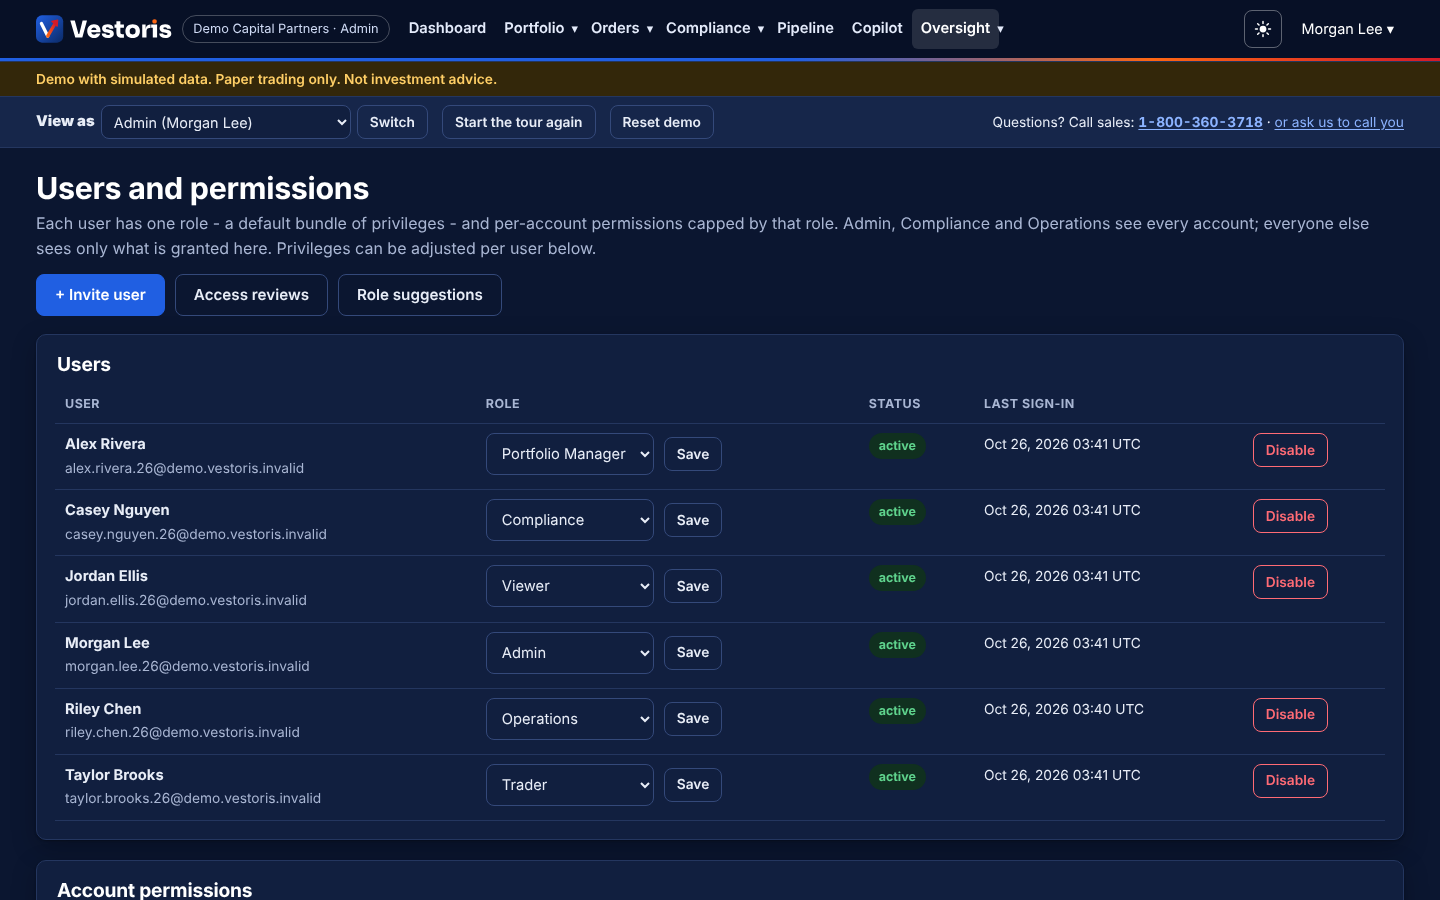
Six roles, adjustable per user
- Trader, Portfolio Manager, Compliance, Operations, Admin and Viewer.
- View, propose, trade and approve, granted per account and capped by the role.
- Privileges such as "author compliance rules", "approve compliance rules", "load data" and "export" adjusted per user; firms are strictly isolated.
Explainable refusals
- "You can view Growth Fund B but do not have trade on it."
- Every refusal names who can grant the permission.
- Every refusal is written to the event log.
Periodic access reviews
- The facts are gathered automatically: every user, role, grant and its use.
- The AI drafts the review and the recommendations.
- An Admin applies the changes they agree with and signs off.
Anomalous access and least-privilege suggestions
- Flags such as a user ordering on an account they normally only view.
- Repeated refusals in a short time.
- Role suggestions from actual use over 90 days.
AI
Where the AI helps
- Drafts the periodic access review.
- Phrases least-privilege recommendations.
Deterministic
What decides
- The entitlement check is code, run server-side on every request.
- Recommendations reference only grants that exist; an Admin applies them.
See it with your own eyes, in ten minutes.
Open a private sandbox firm with sample accounts, rules and orders. No sign-up, no email. Switch roles and follow the guided tour.